IT Security Best Practices and Strategies for Small Businesses in Baton Rouge
What Are the Top Cybersecurity Threats Facing Small Businesses in 2024?
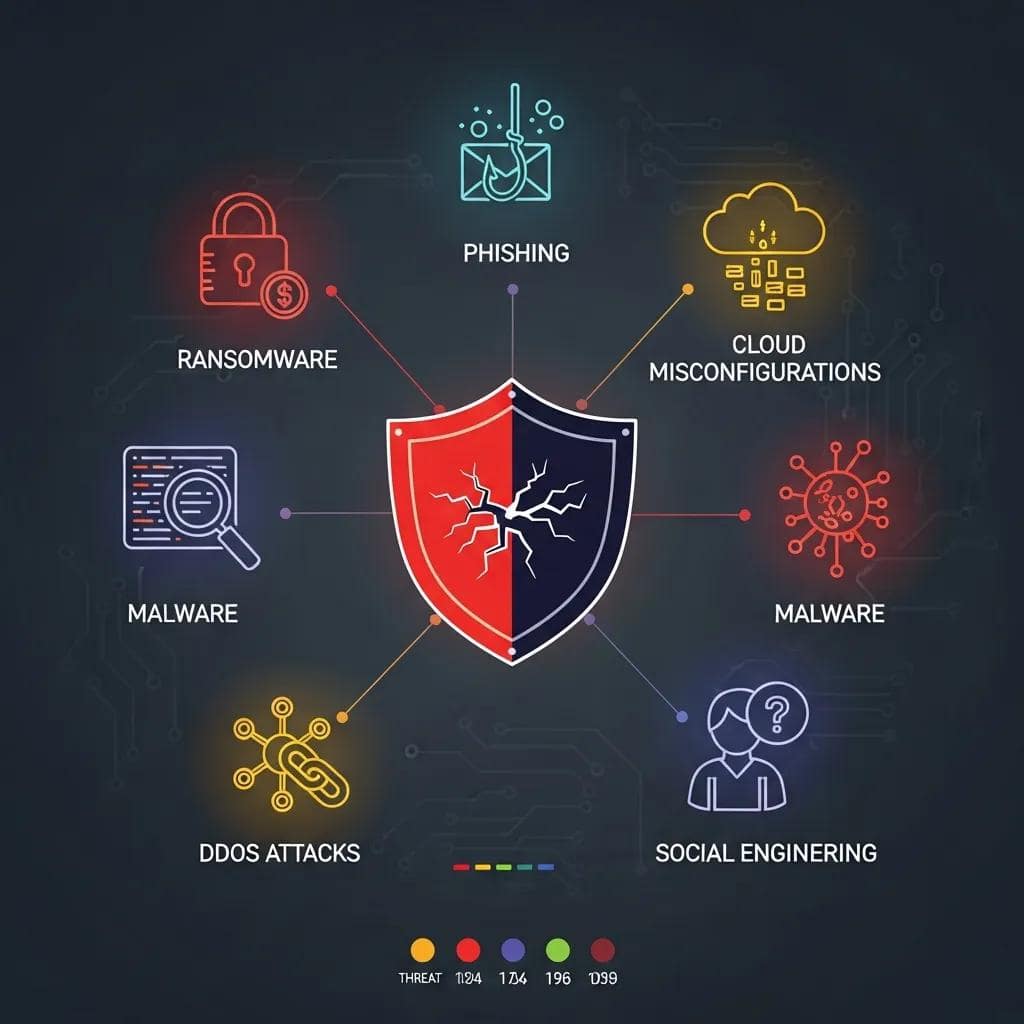
- Ransomware: Use segmented backups and verified recovery to limit downtime and avoid payment pressure.
- Phishing & social engineering: Combine phishing simulations with email filtering and MFA to reduce successful scams.
- Cloud misconfiguration: Enforce IAM controls, configuration reviews, and automated scanning to catch insecure settings.
- Supply chain attacks: Perform vendor risk assessments and require security attestations to limit third-party impact.
- Credential theft: Deploy MFA, password hygiene policies, and monitoring to detect compromised accounts quickly.
How Does Ransomware Impact SMBs and How Can It Be Prevented?
What Are Common Phishing and Social Engineering Attacks to Watch For?
Which Foundational IT Security Best Practices Should SMBs Implement?
- Implement Multi-Factor Authentication (MFA) across administrative and user accounts to prevent unauthorized access.
- Maintain a documented patch management process to reduce exposure from known vulnerabilities.
- Adopt a 3-2-1 backup strategy with regular verification to ensure recoverability after incidents.
- Enforce least-privilege access and role-based permissions to limit lateral movement.
- Run regular cybersecurity awareness training and phishing simulations to reduce human risk.
| Control | Protection Level | Ease of Implementation |
|---|---|---|
| Multi-Factor Authentication (MFA) | High | Moderate |
| Patch Management | High | Moderate |
| Verified Backups (3-2-1) | High | Moderate |
| Least-Privilege Access | Medium-High | Moderate-High |
| Employee Awareness Training | Medium | Easy |
How Can Employee Cybersecurity Awareness Training Reduce Risks?
Why Is Multi-Factor Authentication Essential for Business Security?
How Does Wahaya IT’s Managed Intelligence Enhance Security for Baton Rouge SMBs?
What Benefits Does AI-Driven Threat Detection Provide?
How Are Customized Cybersecurity Solutions Tailored to Local Businesses?
What Are Effective Data Protection and Business Continuity Strategies?
- Maintain verified backups with documented retention and restoration procedures to meet RTO/RPO targets.
- Classify data to prioritize critical systems and ensure sensitive information is encrypted and access-controlled.
- Implement Disaster Recovery as a Service (DRaaS) or hybrid recovery solutions for rapid failover where budgets allow.
| Backup Approach | Typical RTO / RPO | Recommended Solution |
|---|---|---|
| Onsite backups | RTO: hours - days / RPO: minutes - hours | Local NAS with offsite replication and regular verification |
| Cloud backups | RTO: hours / RPO: minutes - hours | Encrypted cloud snapshotting with automated retention policies |
| Hybrid (onsite + cloud) | RTO: under 2 hours / RPO: minutes | 3-2-1 strategy with replication and DRaaS for critical systems |
How Can Robust Data Backup and Disaster Recovery Safeguard Your Business?
What Steps Are Involved in Developing an Incident Response Plan?
How Can SMBs Secure Their Networks, Endpoints, and Cloud Environments?
| Component | Attribute | Managed Service Example |
|---|---|---|
| Firewall | Perimeter and internal segmentation | Managed firewall with rule reviews and threat feed updates |
| Endpoint Protection | Behavioral detection and response | EDR with managed hunting and alert triage |
| Cloud Security | Configuration scanning and IAM monitoring | Cloud posture management and managed CASB services |
What Are Best Practices for Advanced Firewall and Network Segmentation?
How Should Businesses Manage Endpoint Security for Remote Workforces?
What Are the Steps to Partner with Wahaya IT for Comprehensive IT Security?
- Conduct an initial security assessment to identify assets, vulnerabilities, and prioritized risks.
- Develop a custom solution design and remediation roadmap aligned to business priorities.
- Implement controls, migrate systems where required, and validate recovery and detection capabilities.
- Provide ongoing monitoring, patch management, threat hunting, and regular reporting with SLA commitments.